Network Security
Network Security
Attackers Exploit Second Cisco Firewall VPN Zero-Day Since August
Network Security
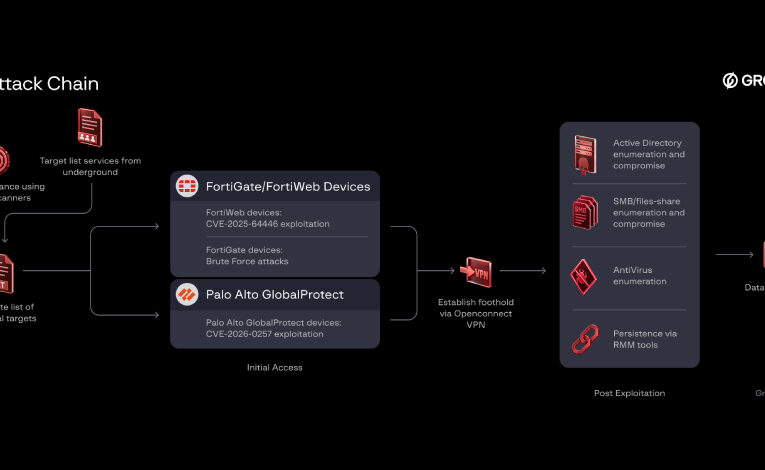
Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials
The Hacker News
Network Security
FortiBleed is still active, with attackers locking admins out of Fortinet firewalls
Network Security
Check Point Discloses Two 9.8-Rated VPN Certificate Flaws Enabling Unauthenticated RCE
The Hacker News
Network Security
The Global Compliance Ripple Effect: How DORA and NIS2 Influence Australian Firms
Cyber Governance Risk And Compliance
Beyond Compliance: Building a Future-Proof Fortress with Architecture, PKI, and APRA CPS 234
Cyber Governance Risk And Compliance
Prompt Injection: The New SQL Injection for the C-Suite
Cyber Governance Risk And Compliance
The End of Session Cookies: Moving Toward Continuous Behavioral Verification
Cyber incident Response and disaster recovery
Curing Alert Fatigue with Predictive Contextualization
Network Security
Tier-N Visibility: Mapping the Nth-Degree of Your Digital Supply Chain
Cyber incident Response and disaster recovery
Agentic Red Teaming: Using AI to Find Your Own Weaknesses
Cloud Technologies
Beyond the Prompt: Securing the Model Context Protocol (MCP) in the Agentic Era
Cyber Governance Risk And Compliance
Cognitive Hacking: The New Frontier of Social Engineering
Cyber Governance Risk And Compliance
The Kinetic Frontier: Securing Physical AI and Autonomous Logistics in 2026
Cloud Technologies
The “Shift Left” Lie: Why Developers Hate Security (And How to Fix It)
Cyber Governance Risk And Compliance
Stop Patching Everything: The Case for “Continuous Threat Exposure Management” (CTEM)
Cyber Governance Risk And Compliance
Offboarding is the New Perimeter: The Insider Risk of Ex-Employees
Cyber incident Response and disaster recovery
Operationalizing Trust: Fixing the Broken Feedback Loop in Modern SOCs
Cyber Governance Risk And Compliance
The Resilient by Design Enterprise: Unifying Strategy, Speed, and Security
Cloud Technologies
The “Toxic Asset” in Your Cloud: Why Data Minimization is Your Best Security Strategy
Cyber Governance Risk And Compliance
API Asset Governance: Identifying and Decommissioning Obsolete Endpoints
Cloud Technologies
Non-Human Identity Management (NHIM) for Multi-Cloud
Cyber Governance Risk And Compliance
Mobile Forensics in the BYOD Era: Privacy vs. Investigation
Network Security
Privacy-Preserving Analytics: Calculating Secrets Without Seeing Them
Cyber Governance Risk And Compliance
Sovereignty Struggles: Investigating Across Borders Without Breaking the Law
Cyber incident Response and disaster recovery
The “Tool Sprawl” Trap: Why More Security Tools Can Mean Less Security
Network Security
Forensic Readiness: Preparation for Investigations
Network Security
Serverless Security: Functions as a Service (FaaS)
Cyber Governance Risk And Compliance
Anonymization vs. Pseudonymization Techniques: A Comprehensive Guide for Modern Data Protection
Cyber Governance Risk And Compliance