ClickFix Attacks Evolve to Better Hide Malicious Payloads
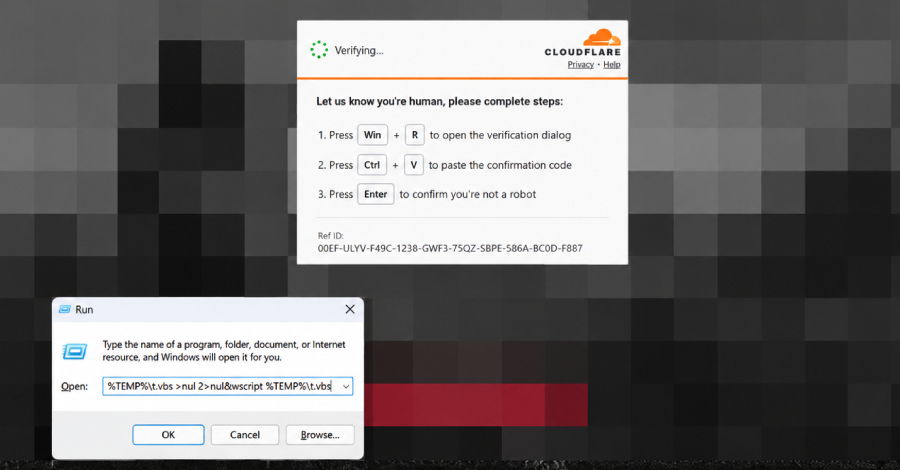
Image: Infosecurity Magazine
ad slot · in-content video 16:9
Coverage
Coverage
- ClickFix sites stage a VBScript payload in the browser cache to bypass the Run dialog's length limit
- Threat actors are now hiding payloads by using DNS TXT records and browser cache pre-fetching, making it tougher to spot early attack stages.
More coverage
- A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's cache. "Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the…