GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address
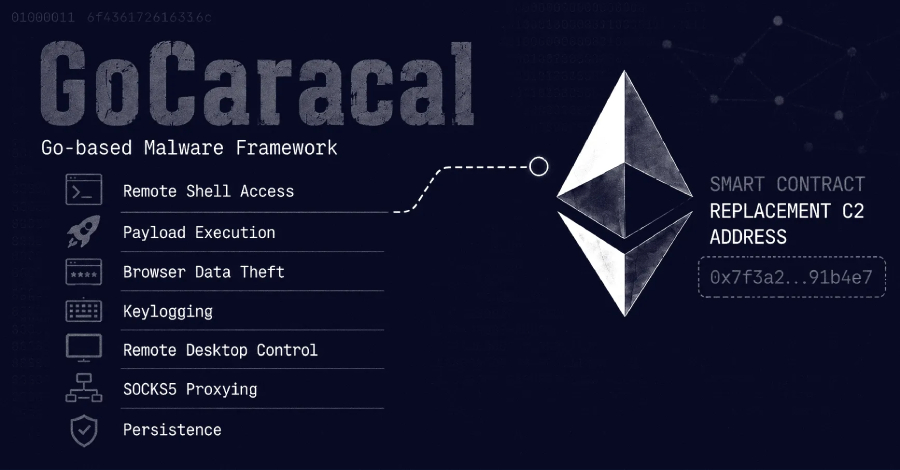
Image: The Hacker News
ad slot · in-content video 16:9
Coverage
More coverage
- Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela. GoCaracal provides operators with remote shell access and…