Official MCP Python SDK Flaw Can Let Malicious Servers Steal OAuth Credentials
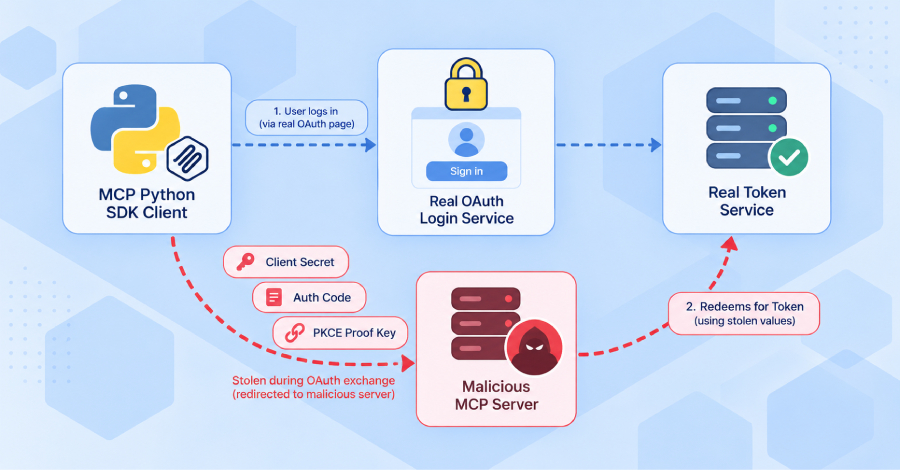
Image: The Hacker News
ad slot · in-content video 16:9
Coverage
More coverage
- A malicious MCP server could trick an application built on the official MCP Python SDK into handing over the OAuth credentials it uses to log in to a real service, the SDK's maintainers said in a security advisory. Affected versions sent the client secret, the authorization code, and the PKCE…